ISO/IEC 27001:2022 certified information security management.
Navionyx Mobility Solutions Private Limited is certified to ISO/IEC 27001:2022 for its Information Security Management System.
Certified by a NABCB accredited certification body.
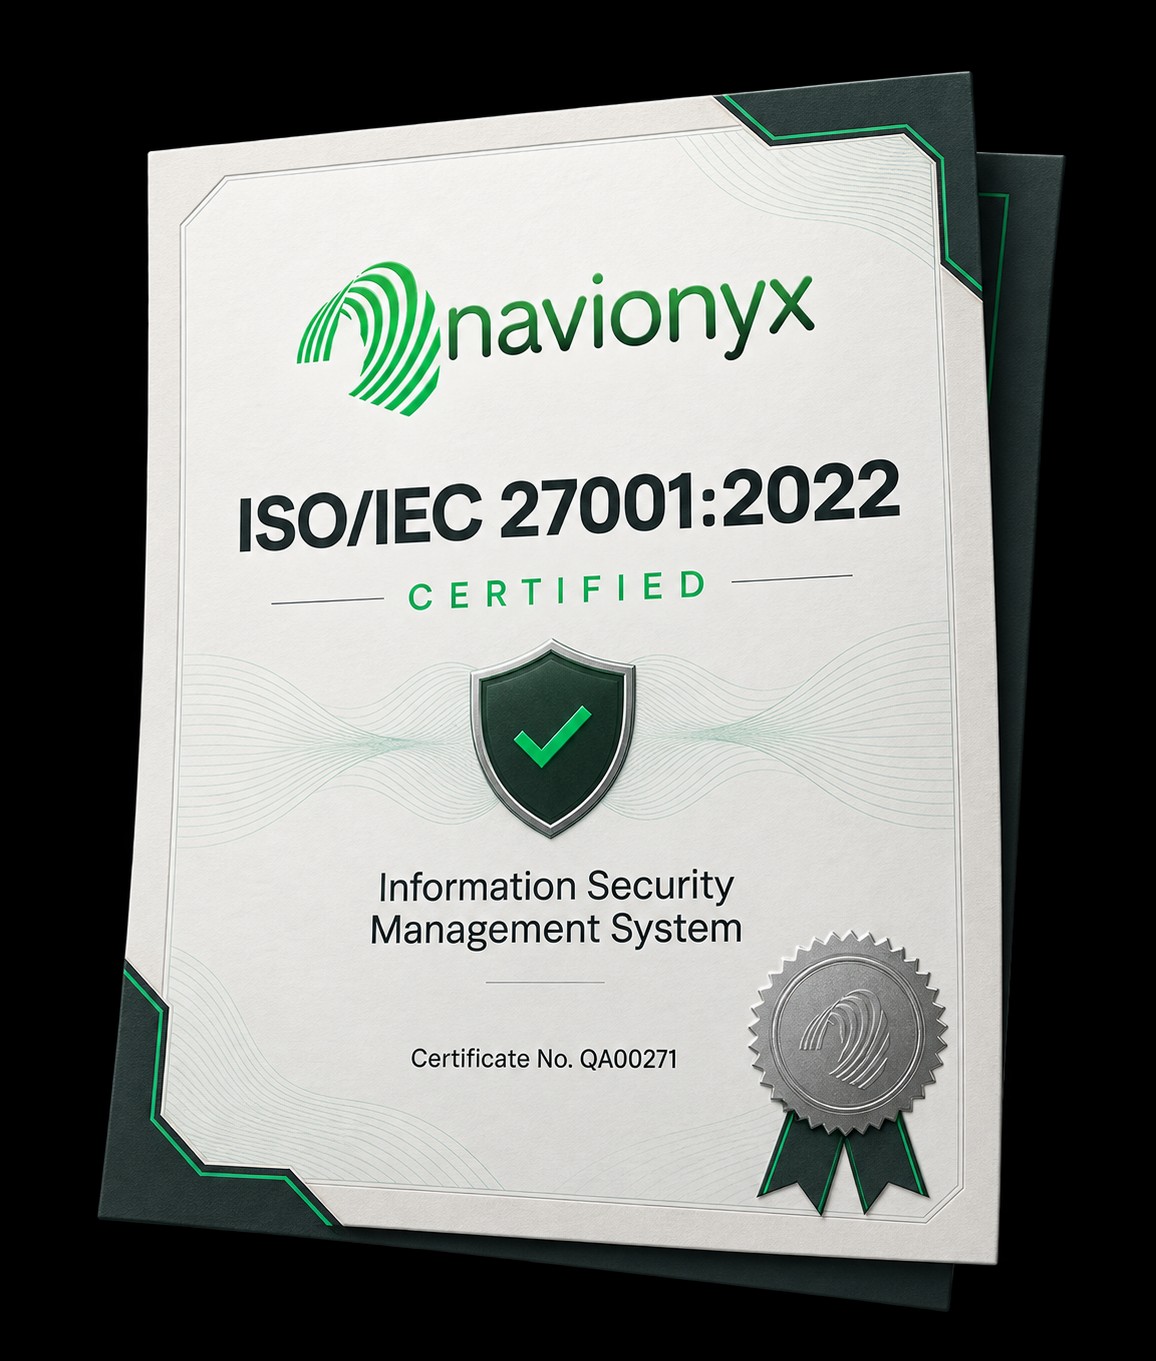
Three layers back this certification.
You do not have to take our word for it. The certificate, the accreditation behind it, and the public record can each be checked independently.
Certificate
Issued by an accredited third party certification body.
Public record
Navionyx’s certification record is publicly available through IAF CertSearch.
Open the record →The record, in full.
Every field below matches the certificate issued to the legal entity and the entry published on IAF CertSearch.
What the certificate covers.
The Information Security Management System applies to the software design and development, operation, maintenance and support of Navionyx SaaS based EV telematics, GPS tracking, fleet management and IoT software solutions, including web applications, mobile applications, APIs, cloud infrastructure, databases, third party technology integrations and customer support services.
Scope wording reproduced exactly as printed on the certificate. Certification applies to the management system. Individual products, GPS devices and customer deployments are not automatically certified.
A three-year cycle with annual surveillance.
Initial certification
ISMS certified to ISO/IEC 27001:2022.
Surveillance audit 1
First annual review of the management system.
Surveillance audit 2
Second annual review of the management system.
Certificate expiry
Recertification audit ahead of renewal.
Certification is a practice, not a document.
The certificate stays valid only while the management system keeps running. These are the controls we operate continuously between audits.
Internal audits and management reviews
Scheduled reviews of controls, findings, and corrective actions.
Risk register and supplier evaluation
Ongoing assessment of information security risk and third-party technology partners.
Incident records and security testing
Documented incident handling with recorded testing across platform and infrastructure.
Employee awareness and access control
Training records and role-based access across systems handling customer data.
Verify our certification independently.
Security questionnaires, vendor registrations, and tender submissions can reference the public IAF CertSearch record and certificate number QA00271 directly.